Turn Your Vision into Success, Let It Fly with Us
Ensure Your Business Is Secure, Compliant & IT-Ready
Create a practical disaster recovery plan for your business using our free editable Word template or PDF guide. Identify critical systems, set recovery priorities, assign responsibilities and prepare your business to recover from unexpected disruption.
Disaster recovery plan template for SMEs
Table of Contents
Why disaster recovery matters for SMEs
- An organisation's Disaster Recovery Plan (DRP) outlines processes for recovering IT systems and data following an issue or disaster.
- Businesses use a DRP to recover from things like ransomware attacks, server failures, or business interruptions.
- IT outages can prevent companies from functioning. For example, Microsoft 365 can experience service outages, which can prevent a business from continuity.
- According to UK Government surveys, SMEs are impacted by cyber incidents each year.
- Ransomware attacks pose one of the biggest risks to businesses when compared to other forms of cybercrime.
- A DRP ensures compliance with UK GDPR requirements and adheres to Cyber Essentials Standards.
- A DRP reduces downtime, minimises the impact of data loss, and helps businesses return to normal after a business disruption occurs.
What Should a Business Disaster Recovery Plan Include?
- A business disaster recovery plan must explain how an organisation will keep operations running and bring back important systems after an unexpected disruption.
A practical plan should include:
- Critical Business Systems: Identify the applications, servers, databases and services that the business depends on.
- Recovery Priorities: Decide which systems must be restored first.
- Recovery Time Objective (RTO): Define how quickly each critical system should be restored.
- Recovery Point Objective (RPO): Establish how data loss the business can accept.
- Backup Arrangements: Document where backups are stored and how they will be protected.
- Responsibilities: Identify the employees and IT providers responsible, for recovery.
- Communication Procedures: Explain how employees customers and suppliers will receive updates.
- Every business has recovery requirements. The business disaster recovery plan should reflect the organisations size, systems and operational priorities.
What is a Disaster Recovery Plan?
- A disaster recovery plan helps your business get IT systems, applications and data back up and running after an unexpected disruption. This could be a ransomware attack, a server failure, accidental data loss or a cloud service outage.
- For UK businesses having a clear written recovery plan can reduce confusion during a crisis. It helps limit downtime and makes sure employees know what to do when important systems stop working.
- Use this free disaster recovery plan template to find out which systems are most important. Set recovery priorities, assign roles and responsibilities. Create a backup and recovery process that works for your business. The template can be changed to fit your organisations size, technology and way of working
- Use this template to document:
- Your IT systems and the order in which they must be recovered.
- The people who must handle recovery and who will communicate during an incident.
- The backup. The steps to restore data.
- The Recovery Time Objectives (RTOs) and Recovery Point Objectives (RPOs).
- The testing schedule, review dates and any follow-up actions.
- Important: The example recovery times and procedures, in this guide are only illustrative. Your business should set its targets based on operational needs, risks, available resources and the abilities of its IT systems
Disaster Recovery Plan Example
See a completed example of a DR Plan for a small UK business, including recovery priorities, responsibilities, and example disaster scenarios.
IT Disaster Recovery Plan Example
Explore a practical IT-focused recovery example covering Microsoft 365, servers, backups, internet failure, cyberattacks and ransomware.
Disaster Recovery Testing Checklist
Use this practical checklist to test your backups, recovery procedures, incident response and business continuity arrangements.
Disaster Recovery vs Business Continuity
| Area | Disaster Recovery | Business Continuity |
|---|---|---|
| Focus | Restoring IT systems | Maintaining business operations |
| Scope | Technical recovery | Organisation-wide response |
| Example | Restoring file servers | Continuing customer support |
| Objective | Recover systems | Keep the business running |
The risks SMEs face without a DRP
Without a documented Disaster Recovery Plan, organisations will likely face:
More time to recover
While determining how to recover, there will be any access for staff to systems.
Loss of data
If there is insufficient data backups, there could be a loss of work done immediately prior to failure.
Business interruption
Business functions such as customer service, finance, and communications are interrupted.
Financial ramifications
Revenue lost due to business interruption, cost of recovering to PRE-incident operations could be substantial.
Non-compliance with regulations
In accordance to UK Data Protection Regulations, organisations need to be able to demonstrate that they manage the data in a responsible manner.
Problems with insurance
Many cyber insurers require proof of backup planning and recovery planning procedures.
Adopting resilience practices as suggested by frameworks such as Cyber Essentials can help the organisation further manage their overall risk.
A step-by-step guide for creating a DRP consists of:
You do not need to have a sophisticated technology set up to put together a Disaster Recovery Plan (DRP). Your most important task is to document the process to restore systems in the event of a disaster.
Step 1: Determine the critical systems used in your environment.
- Make a list of the key IT services your business relies on such as:
- E-mail systems
- File storage
- recovery of servers
- application availability
- network infrastructure
Step 2: Decide the order in which to restore the systems.
The order of restoration can range from those required to conduct business operations, to systems that can withstand a longer outage.
Step 3: Establish your RTO and your RPO.
By determining how long you can go without each system and how much data loss is acceptable, you can develop backup and recovery strategies.
Step 4: Document the recovery process for each system.
Clearly document the procedures for restoring all systems.
Step 5: Determine the people accountable for the recovery process and who provides assistance to them.
Identify the recovery process leader and who will assist.
Step 6: Create a communication process for internal and external clients.
Create a plan to inform employees, clients, and suppliers of developments during a disruption.
Step 7: Test the Plan.
Conduct frequent tests to ensure that your recovery processes will work when they are needed.
Full Disaster Recovery Plan Template
1. Document Control
- Plan Owner:
- Version:
- Last Updated:
- Next Review Date:
2. Key Business Systems
List essential technology platforms.
Example table:
| System | Purpose | Owner | Location |
|---|---|---|---|
| Email platform | Business communication | IT provider | Cloud |
| File storage | Shared documents | Operations | Cloud / Server |
| Accounting software | Financial management | Finance team | Cloud |
3. Recovery Priorities
| System | Priority | Maximum Downtime | Business Impact |
|---|---|---|---|
| High | 4 hours | Communication disruption | |
| File storage | High | 4 hours | Staff unable to work |
| CRM | Medium | 24 hours | Sales delays |
4. Disaster Scenarios
- Identify potential business interruption scenarios; examples are:
- Ransomware attack
- Server failure
- Cloud platform outage
- Power outage at an office
- Internet connectivity problems
- Theft or damage to hardware
5. Recovery Procedures
- Create step-by-step recovery plans for:
- Data restoration
- Server rebuild
- Cloud service recovery
- Email restoration
- Endpoint device recovery
6. Backup Strategy
- Specify key aspects of your backup strategy, such as:
- Backup frequency
- Off-site/cloud location of backup
- Backup encryption
- Backups should be tested for verifiability
- Retention period of backups
7. Incident Response Team
- Examples include:
- Incident lead
- IT recovery lead
- Communications liaison
- Operations manager
- List contact details for:
- Internal staff
- IT provider
- Key suppliers
8. Communication Plan
- In the event of disruption, it is essential to communicate.
- Identify how to notify:
- Employees
- Customers
- Suppliers
- External stakeholders
Recovery Priorities, RTO and RPO: Practical Examples for SMEs
- A disaster recovery plan should explain which business systems need to be restored first, how quickly they must be recovered, and how much data the business can afford to lose.
- Setting clear recovery priorities, Recovery Time Objectives (RTOs) and Recovery Point Objectives (RPOs) helps small and medium-sized businesses make informed decisions during an IT outage, cyberattack, hardware failure or data loss incident.
What Is RTO?
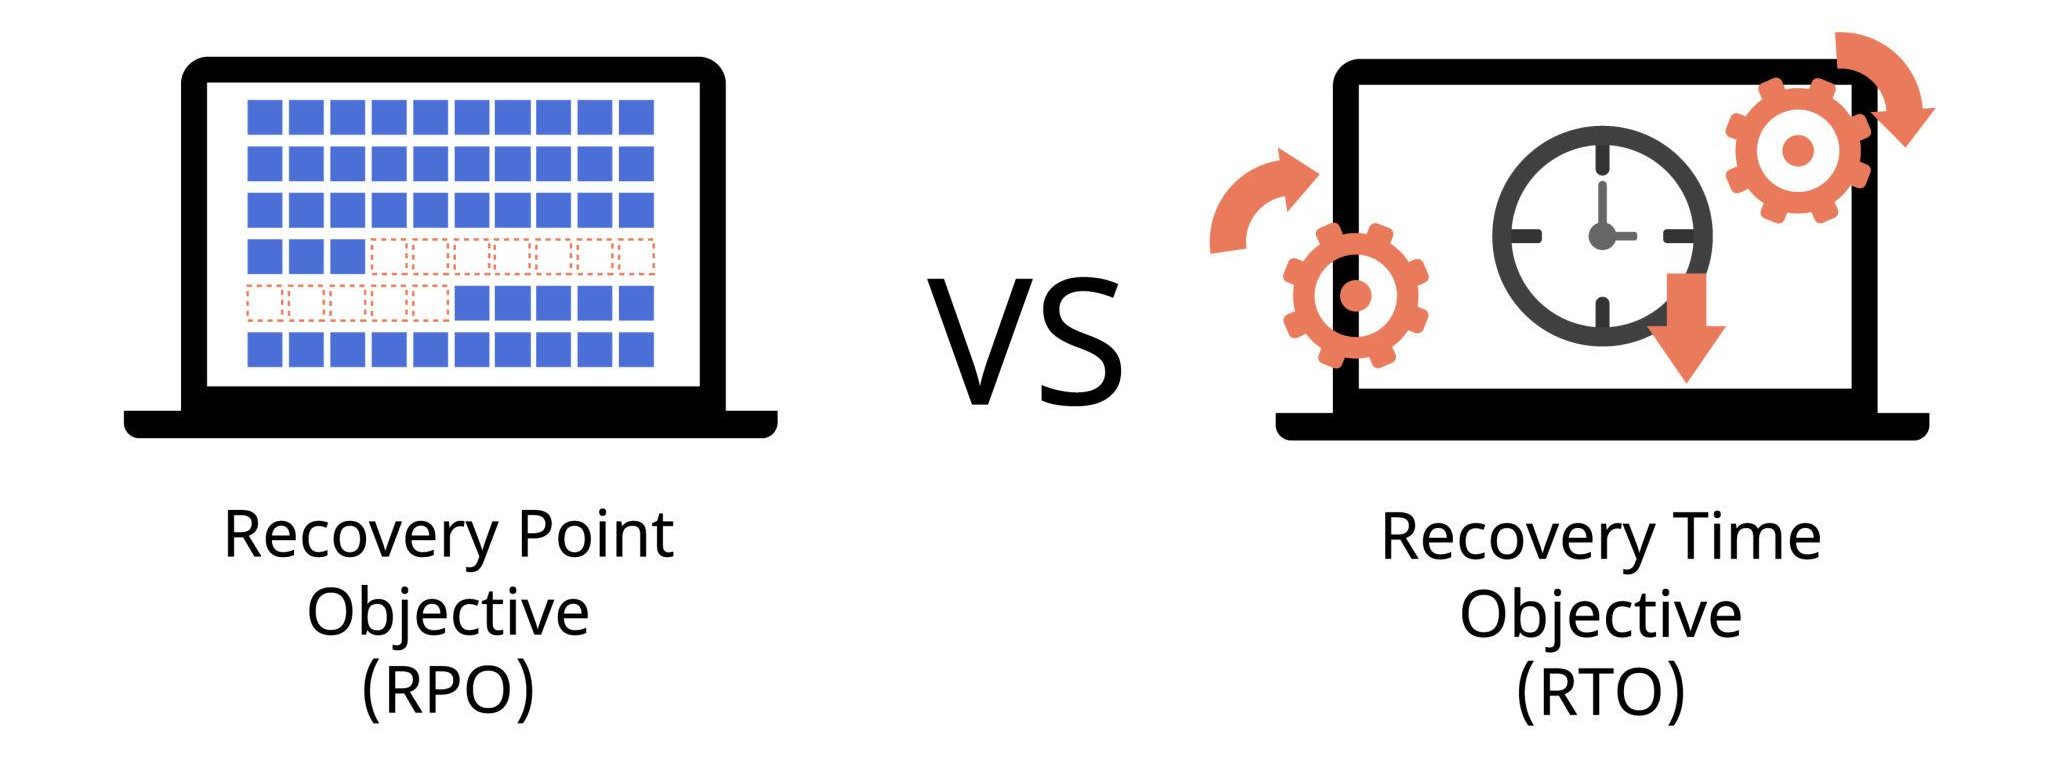
- Recovery Time Objective (RTO) is the target time within which a system or service should be restored after a disruption.
- For example, if your business sets an RTO of four hours for its email service, the recovery team should aim to restore access within four hours of the disruption starting.
What Is RPO?
- Recovery Point Objective (RPO) is the maximum acceptable period of data loss, measured backwards from the time of the incident.
- For example, an RPO of one hour means the business aims to recover data to a point no more than one hour before the disruption. This may require frequent backups, replication or another suitable recovery method.
- Important: RTO and RPO are targets, not guarantees. They should be based on business impact, technical capabilities, backup arrangements and the recovery options available.
Example: Recovery Priorities for a Small Business
- Consider a UK business with 25 employees that uses Microsoft 365, cloud accounting software, a customer relationship management (CRM) system and a shared file storage platform.
- If a major IT incident affects several services, the business should restore systems according to their operational importance and dependencies.
| Priority | System or service | Example RTO | Example RPO | Reason |
|---|---|---|---|---|
| 1. Critical | Identity and administrator access | 2 hours | 1 hour | Recovery teams need secure access to manage affected systems. |
| 2. Critical | Email and staff communications | 4 hours | 1 hour | Staff need to coordinate recovery and communicate with customers. |
| 3. High | Essential business files | 8 hours | 4 hours | Employees need access to operational documents and records. |
| 4. High | Accounting and invoicing | 8 hours | 4 hours | The business needs to manage payments, invoices and financial records. |
| 5. Normal | CRM and non-essential reporting | 24 hours | 8 hours | Some customer management and reporting activities may be temporarily delayed. |
- These figures are illustrative planning targets, not universal standards. Your business should set its own objectives after assessing the impact of downtime and the availability of alternative working arrangements. Some services may need to be restored sooner, and dependencies may change the order.
How to Set Your Recovery Priorities
Identify Critical Business Activities
List the services employees need to serve customers, process orders, receive payments and maintain essential business operations.
Assess the Impact of Downtime
Consider lost revenue, customer commitments, contractual obligations, regulatory responsibilities and potential reputational damage.
Identify System Dependencies
Identify which systems rely on other services. For example, email and accounting software may depend on identity services, internet connectivity or a third-party provider.
Agree RTO and RPO Targets
Consult business owners, department managers and IT support staff to establish realistic recovery time objectives (RTO) and recovery point objectives (RPO).
Confirm Recovery Arrangements
Review backup frequency, restore times, access arrangements, available equipment and supplier recovery commitments to check whether the agreed targets can be met.
Document Recovery Approval
Name the person responsible for setting recovery priorities, approving key decisions and authorising the return to normal business operations.
Review and Update Your Recovery Targets
- Review RTOs and RPOs whenever important systems, suppliers, business processes or working arrangements change. Test whether the targets remain achievable and record any gaps that require corrective action.
Testing and Maintaining a DRP
- A disaster recovery plan is only useful if it is tested on a regular basis. To the extent possible you should use best practices by:
- Testing the backups restoration
- Conducting tabletop simulations of incidents
- Reviewing your recovery process
- Updating the documents when there are changes to your system
- Most commonly, an annual review meets the needs of most small to median companies.
Disaster Recovery Readiness Checklist
- Documenting Critical Systems
- Defining Recovery Priorities
- Implementing a Backup Strategy
- Assigning Responsibilities for Incident Response
- Defining Communication Protocols
- Documenting Recovery Plans
- Testing the Disaster Recovery Plan Every Year
Step 6: Implement a backup strategy.
- Confirming Backup Schedules
- Securing Backup Locations
- Conducting Restoration Checks (Testing Backups)
- Enabling Backup Monitoring
| System | Priority | Maximum Downtime | Business Impact |
|---|---|---|---|
| High | 4 hours | Communication disruption | |
| File storage | High | 4 hours | Staff unable to work |
| CRM | Medium | 24 hours | Sales delays |
FAQs
1. Does the Law Require Disaster Recovery Planning (DRP) in the UK?
There is no legal requirement for a disaster recovery plan, but all businesses must follow UK data protection laws by safeguarding data that is personal.
2. How Often Should You Test a DRP?
In most cases, small and medium-sized businesses should evaluate their DRP at least once a year to determine its effectiveness.
3. Who is Responsible for the DRP?
In most cases, the IT Director, Operations Director, or an external IT vendor is responsible for the disaster recovery plan.
4. What Level of Detail Do I Need to Include in the DRP?
A DRP should have sufficient detail so that all employees can execute the recovery steps when necessary.
5. Are Cloud-Based Backup Services Sufficient for Disaster Recovery?
While they can be valuable, cloud-based backup services need to be verified and tested regularly as part of your disaster recovery plan.
About This Guide
The Computer Support Centre developed this document to assist small to medium-sized UK businesses in developing and executing an operationally sound disaster recovery framework.
This document provides simple tangible guidance for business owners, operations managers, and IT assisting organisations in developing a realistic disaster recovery plan without undue technical complexity.
Instead of emphasising theory, this document provides practical recovery methodologies, checklists, and structured templates designed for UK SMEs. The ultimate aim of this publication is to assist organisations in decreasing overall downtime, safeguarding key data and increasing their organisation’s resiliency towards cyber crime, hardware failure, and any other unforeseen disruption.
Ransomware Recovery Plan for Small Businesses
Ransomware attacks can disrupt business operations, encrypt important files and affect access to critical systems. Read our Ransomware Recovery Plan for Small Businesses for practical steps to isolate affected devices, protect backups and restore business systems safely.
Conclusion
A disaster recovery plan should be considered more than an IT policy it represents a practical safeguard used for the rapid recovery of your organisation when the unexpected occurs. A few hours’ downtime can severely impact your business processes delay the provision of services to your clients; and create a financial loss.
Fortunately, disaster recovery does not have to be complicated: Businesses who have identified their critical systems; agreed on realistic recovery priorities; continue to maintain reliable backups and produce documentation on clear recovery procedures can generally prevent downtime to their operations due to cyber incidents; outages; or hardware failures.
In summary, an effective Disaster Recovery Plan ensures that when a disruption occurs, your employees know in advance what to do who is responsible and how to restore the systems. Simply put, preparing today eliminates confusion tomorrow.