Turn Your Vision into Success, Let It Fly with Us
Ensure Your Business Is Secure, Compliant & IT-Ready
How to Implement a Password Policy in Your Business
- Creating a password policy is the first step. Small businesses must also communicate the rules, configure suitable security controls. Regularly review whether the policy is being followed.
Step 1: Identify Business Accounts
- Create a list of business systems that require authentication, including email, Microsoft 365 accounting software, customer databases, remote access and administrator accounts.
- Identify which accounts contain information or could affect other systems if compromised. Prioritise these accounts when introducing security controls.
Step 2: Customise the Template
- Replace the example details in your password policy template with your business name, policy owner, approval date and review date.
- Clearly define password requirements, password storage rules MFA requirements, account recovery procedures and how employees should report suspected compromise.
- Make sure the policy reflects your business needs and the security features supported by your systems.
Step 3: Configure Security Controls
Work with your IT administrator or support provider to implement technical controls including:
- Enable MFA for important accounts, especially administrator accounts and business email.
- Configure appropriate password requirements and compromised-password protection where available.
- Introduce an approved password manager for storing unique passwords.
- Restrict administrator permissions and review account recovery settings.
- Enable security alerts for sign-ins where supported.
- Check that your technical settings support the written policy. Avoid requiring password changes without a specific security reason; reset passwords promptly when compromise is suspected or confirmed..
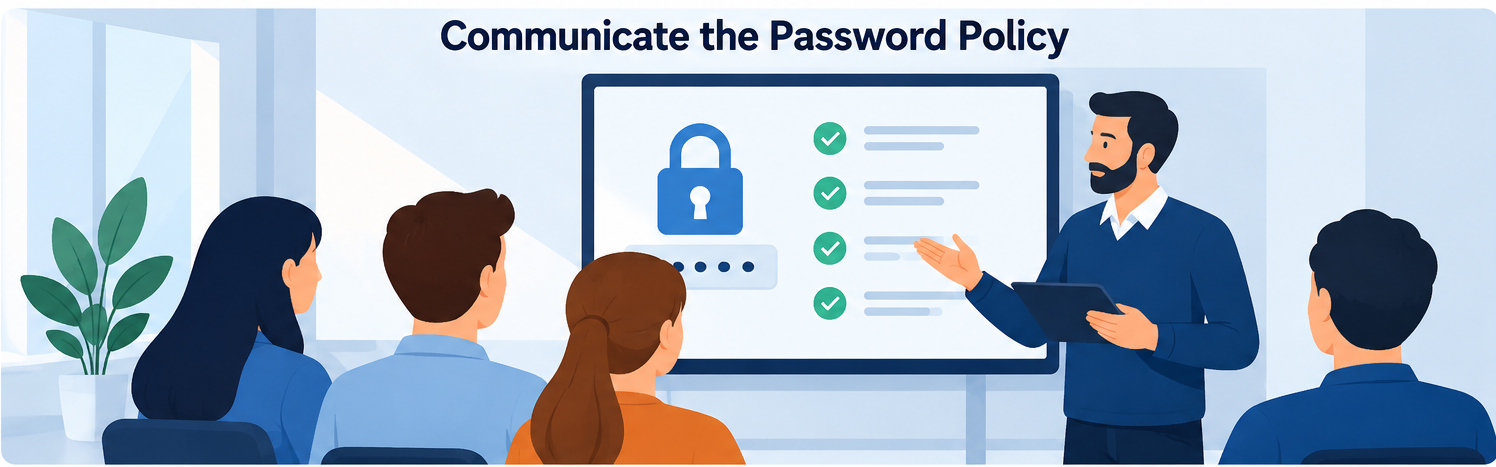
Step 4: Communicate the Password Policy
- Share the approved policy with employees. Explain their responsibilities in simple language.
- Provide guidance on creating passwords using the approved password manager recognising phishing attempts and reporting suspicious account activity.
- Ask employees to acknowledge the policy and record training completion. Never ask employees to share their passwords.
Step 5: Review Access and Compliance
- Regularly check whether the required security controls are enabled and account access is managed correctly.
- Review MFA coverage, administrator permissions, account ownership and access for employees. Check that password recovery procedures are secure. Employees can access the approved password manager.
- Record any gaps, assign actions and prioritise high-risk issues. Use reports and access reviews rather than collecting employees passwords.
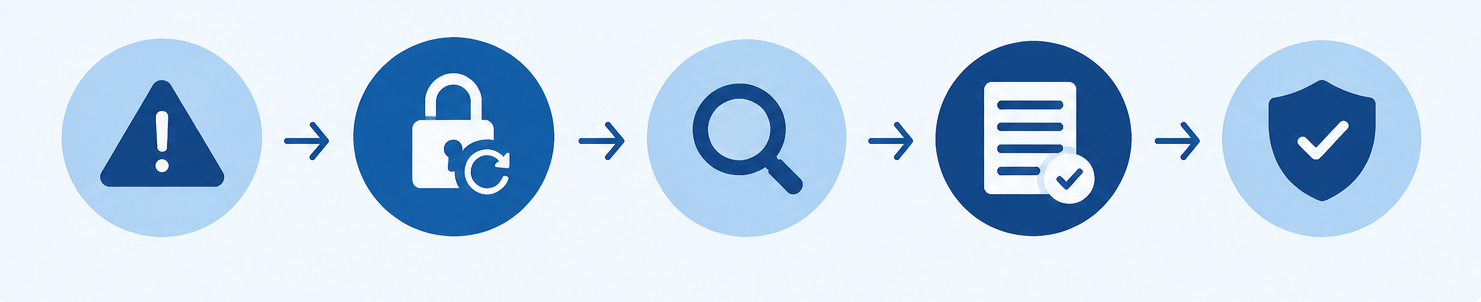
Step 6: Establish a Password Incident Response Procedure
Explain what employees should do if a password is exposed or an account appears compromised.
- Report the incident: Contact the designated IT support team or security contact immediately.
- Secure the account: Reset compromised credentials. Revoke active sessions or tokens where appropriate.
- Check accounts: Assess accounts if the same password has been reused.
- Investigate activity: Review sign-in records. Identify any unauthorised changes.
- Record the outcome: Document the incident actions taken and improvements required.
- If personal data may have been exposed, follow your data breach procedure. Assess any applicable UK reporting obligations.
Step 7: Review and Improve the Policy
- Assign a policy owner and review the document periodically after significant security incidents or changes to business systems.
- Monitor measures such, as MFA coverage, employee training completion, overdue access reviews and unresolved security issues.
- Record the review date identified weaknesses and corrective actions. Update the policy when necessary. Communicate significant changes to employees.
!
Important
A written password policy cannot protect accounts on its own. Effective security depends on technical controls, unique passwords secure account management and employees knowing how to report suspicious activity.